LiteLLM’s New Poisoned Release: Trusted Software Supply Chains Become the Enemy Within
Attackers used compromised LiteLLM owner credentials to exfiltrate repository secrets and later publish malicious Python and container artifacts, demonstrating why enterprise trust must extend across identities, workflows, builds and distributed binaries—not stop at an official repository or package channel.
Take the argument with you.
Read the publication-ready report. Generated from the canonical News article.
What changed
LiteLLM’s investigation connects two stages of a software supply-chain compromise separated by roughly 10 days and 13.5 hours. On October 10, 2026, a malicious GitHub Actions workflow ran in the legitimate BerriAI/litellm repository from a short-lived branch and transmitted repository secrets, including GH_TOKEN, to an attacker-controlled endpoint.1 Socket independently documented the workflow activity and the use of transient branches before the later release compromise.2
LiteLLM says the attacker possessed a GitHub CLI OAuth token belonging to an organization owner, giving the attacker owner-level access across the organization’s repositories. The vendor attributes that access to an Agent Platform master key that had been accidentally committed to a public repository on May 27 and was not revoked. According to LiteLLM, the attacker used that key on October 10 to retrieve the owner’s GitHub token.1 Those details are LiteLLM’s account of initial access rather than an independently established finding.
The compromise became a distribution event on October 21. Seven malicious LiteLLM 1.107.0 wheels were published to PyPI between 11:39:51 and 11:40:13 UTC, followed by compromised Docker Hub and GitHub Container Registry images at 11:46:56 UTC.134 LiteLLM reports that its audit evidence links the GH_TOKEN exfiltrated on October 10 to the token later used to approve the malicious production release.1
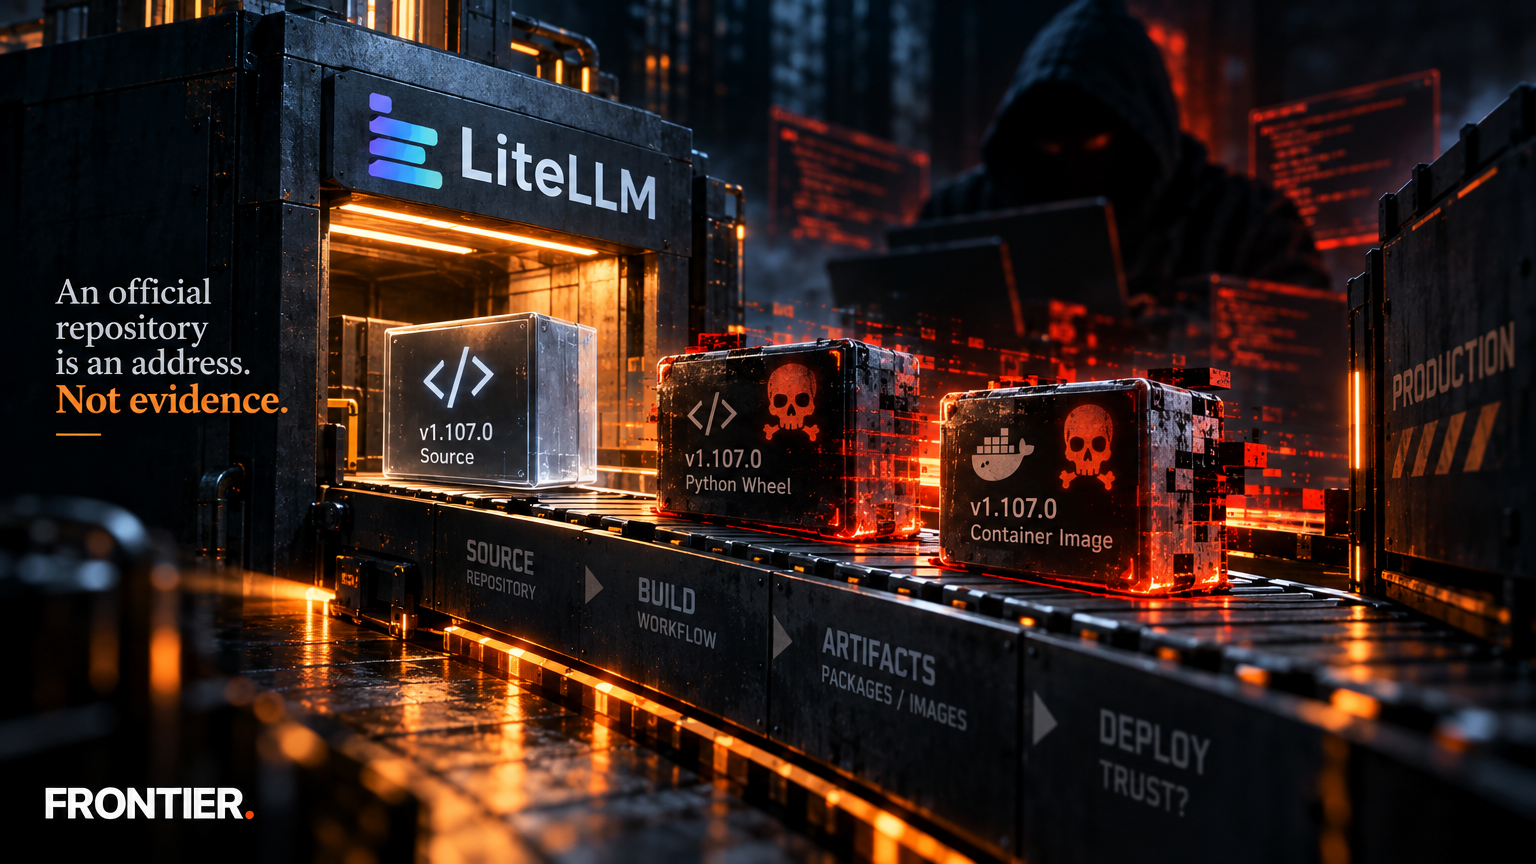
Critically, the poisoned artifacts were built from a lookalike Berri-AI/litellm repository, not from the legitimate BerriAI/litellm source. The official GitHub v1.107.0 source tag did not contain the malicious files found in the distributed packages.354 Microsoft’s independent technical analysis found that the compromised wheels installed Python startup hooks capable of executing a credential collector whenever Python started; an application did not have to import LiteLLM for the code to run.5
Describing the event as a GitHub repository breach is reasonable shorthand, but the more precise account is an identity and release-system compromise: an organization-owner credential enabled unauthorized branch pushes and workflow execution, followed by abuse of release authority.12 The widely used “11 days before” formulation compares the October 10 and October 21 calendar dates. Based on LiteLLM’s timestamps, the interval from the first documented malicious workflow to the first poisoned wheel was approximately 10 days, 13 hours and 28 minutes.1
Why it matters
The incident changes the CIO decision model because familiar trust signals diverged. The legitimate source tag was clean, yet packages and containers distributed under the expected project identity were malicious.35 That means neither an official repository nor an official-looking package channel can independently establish that a deployed artifact came from reviewed source through an authorized build.
Software adoption decisions therefore need two separate assessments. The first is conventional: whether the source, maintainer and dependency are acceptable. The second is provenance: whether each binary, wheel or container can be traced to the authorized source revision, build workflow and release identity. This second assessment is an analytical requirement arising from the documented source-to-artifact mismatch, not a claim that any particular control would have prevented the incident.
The identity layer must also move into the software-risk model. LiteLLM’s account indicates that a key exposed through one platform provided a path to an organization owner’s GitHub token, while the later attack used release authority associated with the exfiltrated repository token.1 For CIOs, the relevant question is no longer simply whether multifactor authentication or branch protection exists. It is whether any credential outside the release system can retrieve, inherit or exercise the privileges needed to alter workflows, access secrets or approve publication.
That shifts evaluation from vendor security features to release-path architecture. A supplier may maintain clean source, review pull requests and publish through recognized registries while still exposing a dangerous gap between those controls. Transient branches, workflow permissions, organization-owner tokens, build inputs and registry publishing rights all become parts of one trust boundary. Socket’s reconstruction of short-lived branch and workflow activity illustrates why controls focused only on long-lived branches or source review can miss the preparatory stage.2
The response model changes as well. Waiting for malware detection in a package is too late if executing the language runtime can activate the payload. Microsoft found that the malicious wheels used Python startup behavior rather than depending on an explicit LiteLLM import.5 The defensible enterprise trigger is consequently a break in provenance or unexpected use of release authority, not solely confirmation of malicious code.
CIOs should treat software provenance as an operating requirement proportionate to deployment exposure. An artifact that can reach production credentials, development secrets or shared runtime environments deserves stronger evidence than a low-impact tool isolated from sensitive systems. This is a risk-based inference from the attack path: the closer a component sits to valuable credentials and automated infrastructure, the more consequential an unverifiable build becomes.
Frontier take
The decisive assertion is that an official distribution channel is an address, not evidence. Trust should be granted only when the artifact presented for deployment can be bound to authorized source, an approved build and a constrained release identity.
LiteLLM 1.107.0 makes that distinction unusually clear. The source tag available from the legitimate repository lacked the malicious files, while the wheels and container images distributed as the release were poisoned.354 A control regime that approved software because it came from the expected repository, package name or registry location would have evaluated the wrong object. The artifact actually entering the enterprise—not the source page an evaluator inspected—carried the risk.
This does not make repositories or package registries irrelevant. It means their signals must be joined. The enterprise needs evidence that the artifact’s origin, build and authorization agree with one another. If an artifact points to source that does not reproduce or account for its contents, or if its release authorization depends on an unexpectedly privileged identity, the trust chain is incomplete even when every endpoint appears official.
The documented interval between the malicious workflow and poisoned release also shows why provenance controls belong in continuous operations rather than procurement questionnaires. Unauthorized workflow activity occurred well before publication, and LiteLLM says the stolen token was later used in approving the malicious release.1 A point-in-time vendor review could not resolve whether a future artifact would follow the approved path. Enterprises need deployment gates and telemetry capable of reassessing that path for each consequential release.
The broader shift is from reputation-based trust to transaction-specific trust. Vendor reputation, repository ownership and registry presence remain useful context, but none answers the critical deployment question: did this exact artifact originate from the source and process the organization intended to trust? The clean-tag and poisoned-artifact split demonstrates that those answers can differ.5
For CIOs, provenance should therefore determine both admission and response. Verifiable lineage supports deployment; absent or contradictory lineage triggers quarantine or additional validation. Unexpected changes to workflows, publisher identities or release authorization should initiate investigation before a malicious payload is independently confirmed. That model aligns the control point with the attack path rather than with the attacker’s eventual code.
Three moves for CIOs
-
— Make source-to-artifact divergence a production stop condition Require teams to verify that consequential wheels, containers and other binaries are traceable to an approved source revision and build path before production admission. Record the expected source, builder and release identity together; quarantine an artifact when those records are absent or contradictory rather than accepting the package name or registry location as sufficient evidence.
- Decision trigger: Block or escalate deployment whenever an artifact cannot be tied to the approved source tag, contains material not accounted for by that source and build, or arrives through a publisher or build path different from the one approved for the supplier.
- Why now: LiteLLM’s legitimate v1.107.0 source tag was clean while the distributed wheels and images were malicious.35 That separation makes source review alone an inadequate release decision and turns provenance mismatch into an actionable risk signal.
-
— Model release authority as a cross-platform privilege graph Map every human token, OAuth grant, service credential and external platform key that can retrieve repository credentials, change workflows, access release secrets or approve publication. Separate routine organization ownership from release authorization, and require review when one credential can cross multiple stages of the source-to-artifact path.
- Decision trigger: Redesign or suspend a release path when an external master key can retrieve a source-control owner token, when an owner credential can directly authorize publication, or when the same credential can both alter build inputs and approve the resulting release.
- Why now: LiteLLM attributes initial access to an exposed Agent Platform key that was allegedly used to retrieve an organization owner’s GitHub token, while its audit account links a subsequently exfiltrated token to the malicious release approval.1 The reported chain shows why credentials must be evaluated by combined reach, not one system at a time.
-
— Begin incident response at the first provenance break Correlate ephemeral branch creation, unexpected workflow execution, repository-secret access, publisher-identity changes and artifact-to-source mismatches. Preserve the associated audit evidence and pause affected releases while responders determine whether build or publication authority has been compromised.
- Decision trigger: Initiate the response workflow when an unapproved branch executes automation with secret access, a release uses an unexpected identity or repository, or a published artifact no longer matches its authorized source—even if malware analysis has not yet confirmed a payload.
- Why now: The documented malicious workflow preceded the poisoned wheels by approximately 10 days and 13.5 hours, creating a potential intervention window before distribution.12 Because Microsoft found that Python startup alone could activate the credential collector, waiting for application-level behavior would place detection after exposure.5
Sources
- LiteLLM canonical root-cause analysis: The attack chain behind the v1.107.0 release 1
- LiteLLM incident notice for compromised release 1.107.0 3
- Socket investigation of secret-stealing workflows executed before the release attack 2
- Microsoft Security technical analysis of the LiteLLM 1.107.0 payload 5
- The Register reporting on the LiteLLM supply-chain compromise 4
[^litellm-rca][^socket-research][^litellm-incident][^register-report][^microsoft-research]